AI agents are moving beyond answering questions and generating content. They can retrieve information, interact with business systems and carry out multi-step tasks with limited human intervention. For enterprises, the opportunity is significant: agents could help resolve service requests, process invoices and coordinate work across departments.
But giving an AI agent the ability to act introduces a different challenge from simply using AI to generate an answer. What happens when it accesses the wrong data, makes an unauthorised change or completes a task incorrectly at scale?
The answer is not to prevent agents from acting. It is to establish clear boundaries around what they can do, how their performance is measured and when a person must intervene.
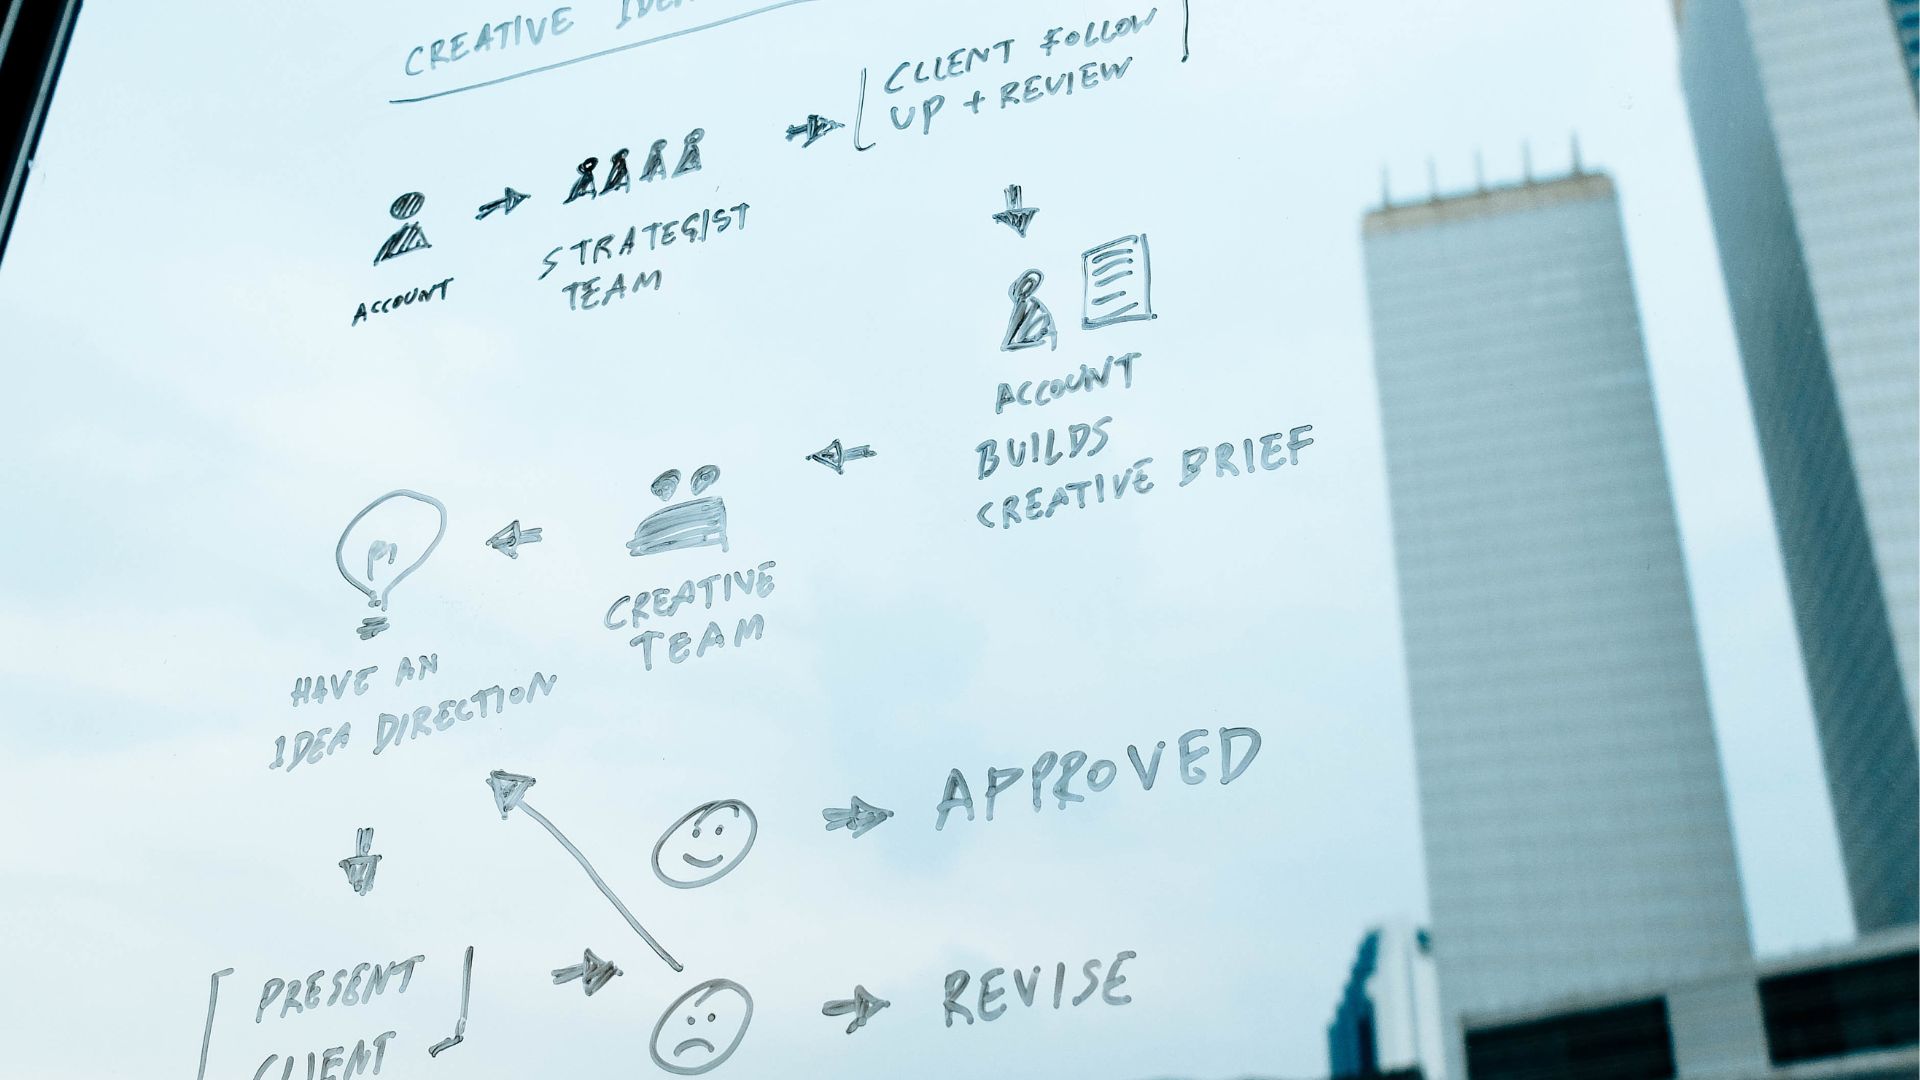
Before deploying an agent, organisations should identify the business process it is intended to improve. This means understanding the steps involved, the systems and data it requires, the decisions it may influence and the consequences of getting something wrong.
An agent that summarises internal reports carries a different level of risk from one that approves payments or changes customer records. Treating both in the same way can lead to unnecessary restrictions in low-risk applications and insufficient oversight in high-risk ones.
The World Economic Forum’s AI Agents in Action: A Playbook for Trusted Adoption, Authorization and Scaling highlights the importance of defining and enforcing the authority delegated to each agent.
A practical starting point is to document four things: the agent’s purpose, the actions it is permitted to take, the actions it must never take, and the conditions under which it must escalate to a human.
An agent can only be governed effectively if its permissions are controlled. Connecting it to multiple enterprise systems without clear restrictions creates unnecessary exposure, particularly when those systems contain sensitive information or support critical business operations.
The principle of least privilege offers a straightforward rule: give each agent access only to the information, tools and functions required for its assigned task. Permissions should be specific to its role, rather than inherited from a broad user account. Access should also be reviewed when the agent’s purpose or responsibilities change.
The Australian Cyber Security Centre’s guidance on agentic AI harnesses emphasises controls such as restricted access, activity logging, monitoring and human oversight. These safeguards help organisations manage risks arising from how agents interact with data and connected systems.
Not every action needs manual approval. Routine, reversible tasks may be automated within defined limits. Actions involving payments, sensitive customer information or significant operational changes may require explicit authorisation before execution.
The objective is proportionate control: enough freedom for the agent to be useful, without granting authority beyond what the task requires.
Governance cannot stop once an agent goes live. Organisations need to understand what it is doing, whether it is following the rules and how its actions affect the wider process.
This requires maintaining records of significant decisions, system interactions, exceptions and human interventions. Monitoring should also flag unusual behaviour, repeated failures and actions that fall outside approved limits. Teams need a clear way to pause an agent, revoke its access or return work to a human when something goes wrong.
Just as importantly, performance must be measured against the original business objective. Faster processing is not necessarily an improvement if error rates, rework or customer complaints increase.
Useful measures could include processing time, first-time-right rates, exception volumes, compliance with business rules and cost per completed case. Comparing these measures before and after deployment helps establish whether the agent is improving the process rather than simply completing more tasks.
AI agents may execute work, but responsibility for their use remains with the organisation. Every agent should have a named business owner, alongside clearly defined responsibilities for technology, security, risk and compliance teams.
The owner should understand the agent’s remit, review its performance and ensure that changes to its model, tools, permissions or operating environment trigger appropriate reassessment.
The APQC guidance on planning, supervising and reviewing AI agents similarly stresses defined roles, permitted actions, human-review requirements and performance measures.
This is particularly important when agents operate across departmental boundaries. A single agent may interact with several systems, but that does not mean accountability should become fragmented or unclear.
AI agent governance is not a once-off approval exercise. Agents need to be reviewed as business processes change, new risks emerge and their responsibilities expand. An agent that performs reliably in a limited pilot may require additional safeguards before being introduced across multiple departments.
Process intelligence can support this work by providing visibility into how processes actually run, where exceptions occur and whether automation is producing the intended results. It can help organisations identify suitable use cases, establish a baseline for performance and monitor the impact of agents after deployment.
The aim is not to add layers of control for their own sake. It is to make autonomous work reliable, traceable and accountable.
The organisations most likely to benefit from AI agents will be those that pair greater autonomy with a clear understanding of their processes, enforceable limits and evidence that the technology is delivering value.
─────────────────────────────────────────────────
What is AI agent governance?
AI agent governance is the framework of policies, permissions, responsibilities and monitoring controls that determines how AI agents are deployed, what actions they can take and how their behaviour is overseen.
What is the difference between AI governance and agentic AI governance?
AI governance covers the broader management of AI risks, including data, models, fairness, security and compliance. Agentic AI governance places additional emphasis on delegated authority, tool access, autonomous actions, workflow boundaries and the ability to intervene in an agent's execution.
How can businesses prevent AI agents from taking unauthorised actions?
Businesses can use unique agent identities, least-privilege access, approved tool integrations, transaction limits, mandatory approval gates and technical restrictions on prohibited actions. These controls should be tested and monitored in production.
How does process mining support AI agent governance?
Process mining reconstructs actual process execution from event data, helping organisations identify deviations, exceptions and bottlenecks. It can complement agent-level logs by showing how an agent's actions affect the wider business process.
Should every AI agent require human approval?
No. The appropriate level of oversight depends on the action's risk, reversibility and business impact. Low-risk activities may be automated within defined boundaries, while consequential or unusual actions may require human review.


Get Updates and announcements from the Verdant Data Team
You can unsubscribe any time. Learn more about our Privacy Policy